What do web application testing solutions test?
Web applications play an important role in modern life. People use them to shop online, manage bank accounts, communicate with colleagues, book appointments, and access important information. Because users expect these applications to work smoothly, businesses must ensure their websites and web-based systems are reliable, secure, and easy to use. 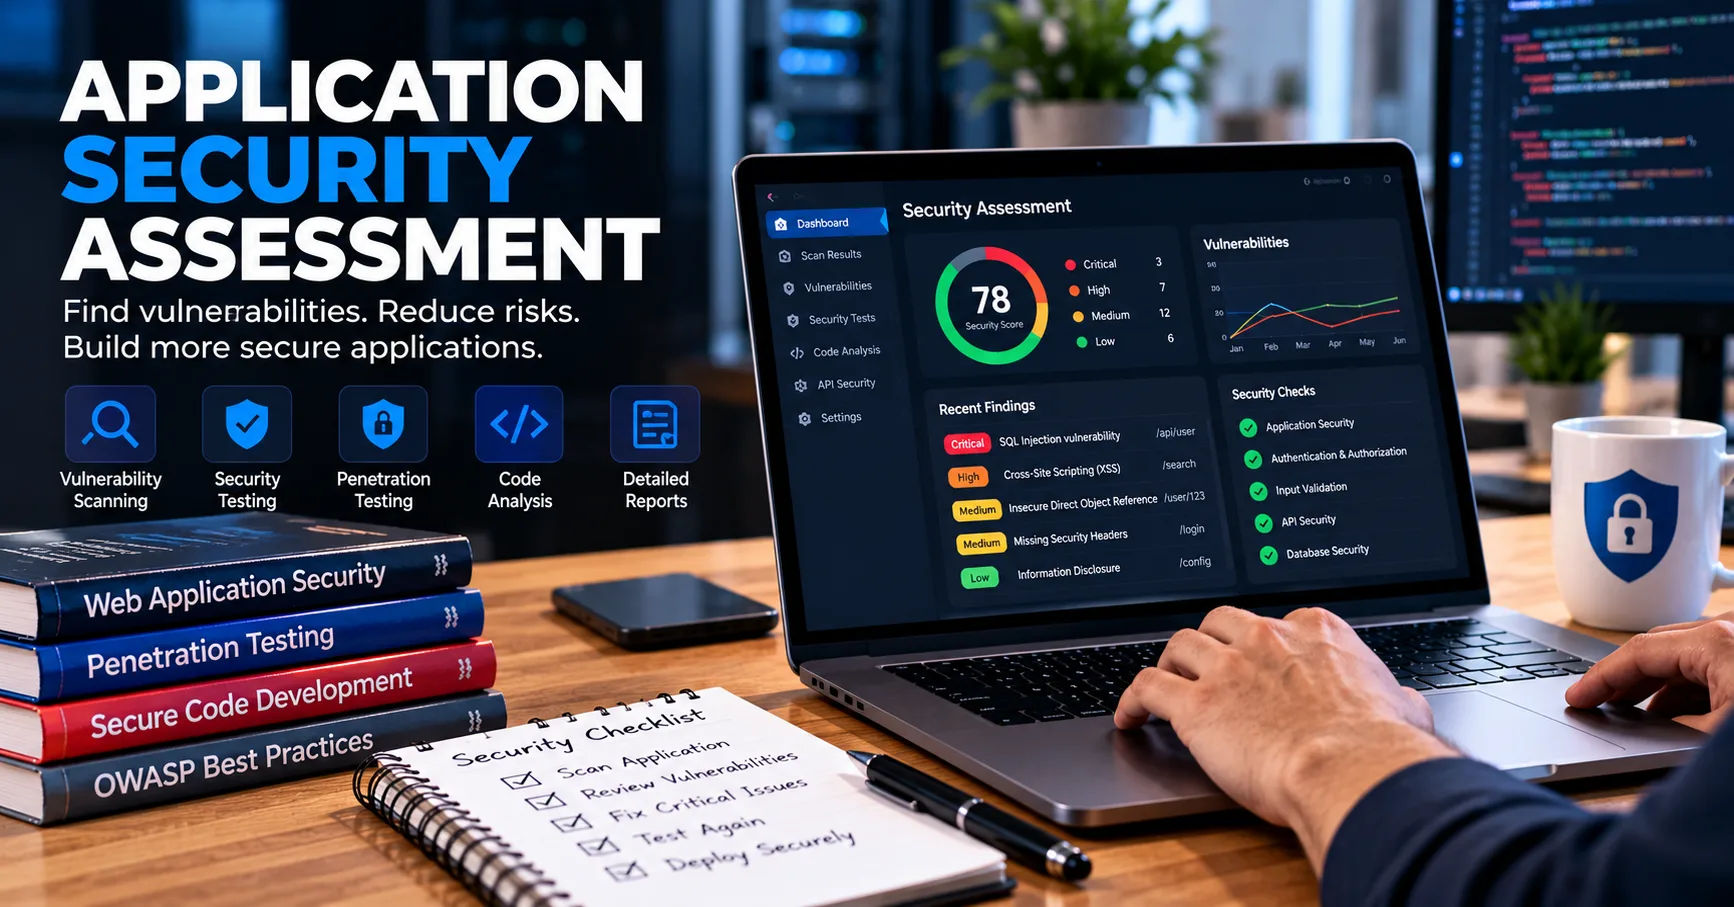 This is where web application testing solutions become essential. They help development teams identify problems before an application reaches its users and reduce the risk of unexpected failures.
Testing involves much more than checking whether a website opens correctly. A web application may contain login forms, payment systems, databases, interactive features, and connections to external services. Every component must work as expected, even when many users access the application simultaneously.
In particular, web application testing solutions examine different aspects of an application, including functionality, performance, security, compatibility, usability, and data handling. These tests help developers understand how an application behaves under normal conditions and when something goes wrong. By identifying weaknesses early, businesses can improve software quality, protect sensitive information, and deliver a better user experience.
Understanding what these solutions test can help business owners, developers, testers, and project managers choose the right testing methods for their needs. The following guide explains the main testing areas, how they work, and why each one matters.
Web Application Testing
web application testing solutions is the process of evaluating a browser-based application to determine whether it meets its requirements. Testers examine its features, design, technical behavior, and ability to handle different situations.
The purpose is to discover defects before they affect real users. These defects may include broken buttons, incorrect calculations, slow page loading, security weaknesses, or problems that appear only on particular devices.
Testing can be performed manually, automatically, or through a combination of both methods.
Manual testing involves a person interacting with an application and checking its behavior. Automated testing uses scripts and specialized software to perform repeatable checks. A combination of these approaches provides broader coverage and helps teams find problems more efficiently.
1. Functional Testing
Functional testing checks whether an application's features work according to the requirements. It focuses on what the application does rather than how quickly or efficiently it performs those tasks.
For example, an online store should allow customers to search for products, add items to their carts, enter shipping information, and complete purchases. Functional testing verifies that each step behaves correctly.
Form and Input Validation
Forms are common in registration pages, contact pages, checkout processes, and account settings. Testers check whether forms accept valid information and reject incorrect or incomplete entries.
For example, a registration form should identify a missing email address or an invalid password. It should also display understandable error messages instead of failing without explanation.
Testers may enter unusually long text, unexpected characters, empty fields, or invalid dates to discover weaknesses in input handling.
Navigation and Interactive Elements
Functional tests also examine menus, links, buttons, search boxes, filters, and other interactive components.
A navigation link should take users to the correct destination. A search feature should return relevant results, while a filter should narrow those results according to the selected conditions.
These checks ensure that users can complete their intended tasks without confusion or unnecessary effort.
Business Logic and Calculations
Applications often contain rules that determine prices, discounts, account permissions, shipping fees, or subscription charges.
Testers verify that these rules produce accurate results. For instance, a shopping application should calculate discounts correctly and apply taxes according to its configured requirements.
Incorrect business logic can lead to financial losses, customer complaints, and inaccurate records.
2. Security Testing
Security testing identifies weaknesses that attackers could exploit to access information, change records, or disrupt application services.
This testing is especially important for applications that process financial transactions, personal information, customer accounts, or confidential business data.
Authentication and Authorization
Authentication checks whether a user is who they claim to be. Authorization determines which resources or actions that user is permitted to access.
Testers examine login procedures, password recovery, session management, and access permissions.
For example, an ordinary customer should not be able to open an administrator's dashboard simply by changing a URL. Similarly, a user should not be able to access another customer's private order information.
Common Security Vulnerabilities
Security assessments may look for several types of weaknesses, including:
-
SQL injection, which can occur when database queries handle untrusted input unsafely.
-
Cross-site scripting (XSS), which can allow malicious scripts to run in a user's browser.
-
Cross-site request forgery (CSRF), which can trick an authenticated browser into submitting unwanted requests.
-
Broken access control, which allows users to perform actions beyond their permissions.
-
Weak session management, which may expose accounts to unauthorized access.
-
Sensitive data exposure, which can result from inadequate protection of confidential information.
Security testing can include automated scanning, manual investigation, and controlled penetration testing. No single technique identifies every vulnerability, so multiple methods are often necessary.
Data Protection and Privacy
Testers also check whether sensitive information is handled appropriately. Passwords should not be stored in plain text, confidential information should not appear unnecessarily in application logs, and protected pages should use appropriate access controls.
Encryption, secure cookie settings, and proper session expiration are additional areas worth examining.
3. Performance Testing
Performance testing evaluates how an application responds to user activity. It helps teams determine whether pages, APIs, and other components operate within acceptable time limits.
An application may function correctly when accessed by one person but become slow when hundreds or thousands of users connect simultaneously.
Load Testing
Load testing measures application behavior under an expected level of user activity.
For example, a ticket-booking website may need to support many customers when tickets become available. Load testing helps determine whether the application can handle that demand without excessive delays or errors.
Stress Testing
Stress testing pushes an application beyond its expected operating capacity. The objective is to identify breaking points and understand how the system behaves under extreme conditions.
Testers observe whether requests fail, response times increase sharply, or the application becomes unavailable. They may also evaluate whether the application recovers after the excessive load ends.
Response Time and Resource Usage
Performance checks measure response times, throughput, error rates, and resource consumption.
Developers may examine CPU usage, memory consumption, database performance, and network activity to locate bottlenecks.
These findings help teams optimize inefficient queries, reduce unnecessary processing, and improve the application's overall responsiveness.
4. Compatibility Testing
Compatibility testing checks whether an application works consistently across different browsers, devices, operating systems, and screen sizes.
Users do not all access applications in the same way. Some use desktop computers, while others rely on smartphones or tablets. Different browsers may also interpret certain features differently.
Browser Compatibility
Testers may evaluate an application in browsers such as Chrome, Firefox, Safari, and Edge, depending on the intended audience.
They check whether layouts, buttons, forms, menus, and interactive features behave consistently.
A page that works perfectly in one browser might display incorrectly in another because of differences in browser engines, supported features, or rendering behavior.
Device and Operating System Compatibility
Mobile devices introduce additional challenges, including smaller screens, touch interactions, changing orientations, and limited resources.
Compatibility testing verifies that important features remain usable on supported devices and operating systems.
It may also examine whether the application handles different screen resolutions, accessibility settings, and mobile browser behavior appropriately.
Responsive Design
Responsive design allows an application's layout to adapt to different screen sizes.
Testers check whether text remains readable, images fit their containers, navigation remains accessible, and forms can be completed without excessive scrolling or horizontal movement.
These checks help deliver a consistent experience to users regardless of their preferred device.
5. Usability and Accessibility Testing
An application can be technically correct and still frustrate users. Usability testing examines how easily people can understand and navigate its features.
Accessibility testing focuses on whether people with different abilities can use the application, including individuals who rely on assistive technologies.
User Experience and Navigation
Testers examine whether users can find important information, understand instructions, and complete common tasks without unnecessary difficulty.
For example, an online booking system should make available dates, prices, and confirmation details easy to locate.
Confusing menus, unclear labels, and complicated forms can cause users to abandon an application even when its underlying functionality works correctly.
Accessibility Features
Accessibility testing may examine:
-
Keyboard navigation without requiring a mouse.
-
Appropriate labels for form fields and buttons.
-
Alternative text for meaningful images.
-
Sufficient color contrast between text and backgrounds.
-
Clear focus indicators for interactive elements.
-
Logical heading structures and readable error messages.
-
Compatibility with screen readers.
Automated accessibility checkers can identify many common problems, but human evaluation remains important. Some issues depend on context and cannot be judged reliably by automated tools alone.
6. Database and Data Integrity Testing
Most web applications depend on databases to store information such as user accounts, orders, bookings, inventory, and transaction records.
Database testing checks whether information is stored, retrieved, updated, and deleted correctly.
Data Accuracy and Consistency
Testers verify that information remains accurate as it moves through the application.
For example, when a customer updates a delivery address, the new address should appear wherever the application is expected to use it. The system should not accidentally overwrite unrelated information.
Data integrity checks also help detect missing records, duplicate entries, and incorrect relationships between database tables.
Database Transactions
Applications often perform several database operations as part of one task. An online purchase, for instance, may create an order, update inventory, and record payment status.
Testing should verify that these operations remain consistent when a process succeeds or fails.
If an operation is interrupted, the application should avoid leaving records in an invalid state. Transaction handling, rollback behavior, and duplicate-request protection may all require examination.
Data Validation and Recovery
Testers examine whether the application rejects invalid data and responds appropriately to database errors.
Depending on the application's needs, testing may also cover backup restoration, recovery procedures, and the handling of temporary database outages.
These checks help protect important records and reduce the consequences of unexpected failures.
7. API and Integration Testing
Web applications frequently communicate with external services and internal components through application programming interfaces, commonly called APIs.
Examples include payment gateways, shipping providers, mapping services, authentication systems, and email platforms.
Integration testing checks whether these components exchange information correctly.
API Request and Response Validation
Testers verify that APIs receive the correct information and return the expected results.
They may check response codes, data formats, required fields, authentication requirements, and error messages.
For example, a shipping API should receive accurate delivery details and return a valid shipping estimate when the request meets its requirements.
Third-Party Service Integration
External services may become unavailable, respond slowly, or change their behavior. Testing examines how the application handles these situations.
A payment integration, for instance, should distinguish between successful payments, declined transactions, and requests that time out without a clear result.
The application should avoid treating an uncertain payment status as a confirmed success or charging a customer repeatedly because of duplicate requests.
Error Handling and Reliability
Integration tests verify whether failures are reported appropriately and whether the application can continue operating when a nonessential service is unavailable.
Depending on the design, useful safeguards may include timeouts, retries, fallback behavior, and clear error messages.
8. Regression Testing
Regression testing checks whether recent changes have accidentally broken existing features.
Developers regularly modify applications to introduce new functionality, fix defects, improve security, or update dependencies. Even a small change can affect other components.
For example, changing a checkout form might unintentionally prevent customers from applying discount codes or selecting a delivery option.
Regression tests repeat important checks after changes are made. Automated test suites are particularly valuable because they can run frequently and provide quick feedback.
What Regression Tests Cover
The scope depends on the change, but regression testing may include:
-
Essential user journeys, such as signing in and completing a purchase.
-
Previously reported defects.
-
Payment and database integrations.
-
Permissions and account settings.
-
Important calculations and validation rules.
-
Features that depend on modified components.
A well-maintained regression suite helps teams release updates with greater confidence.
9. Reliability and Recovery Testing
Reliability testing examines whether an application continues to operate consistently over time. Recovery testing evaluates how well it returns to normal operation after failures.
These tests are particularly important for applications that support business-critical services.
Error Recovery
Testers may simulate interrupted network connections, unavailable services, application restarts, or temporary database failures.
They examine whether the application displays useful messages, preserves valid information, and resumes operations safely.
For example, a user should not lose an entire form unnecessarily because a temporary connection problem occurs.
Long-Term Stability
Some problems only appear after an application has been running for an extended period.
Long-duration testing can help reveal memory leaks, accumulating resource consumption, degrading response times, and other stability issues.
Recovery checks may also evaluate whether backups can be restored and whether essential services can resume within acceptable limits.
10. Automated Testing and Continuous Integration
Automation is not a separate quality dimension in the same way as security or performance testing. Instead, it is a method for executing tests repeatedly and efficiently.
Modern development teams often integrate automated tests into continuous integration and continuous delivery workflows.
Unit, Integration, and End-to-End Tests
Different automated tests examine different levels of an application.
Unit tests check small pieces of code, such as individual functions or calculation rules. Integration tests examine interactions between components. End-to-end tests simulate complete user journeys through the application.
For example, an end-to-end test might sign in, search for a product, add it to a cart, and verify that checkout displays the correct order information.
Choosing What to Automate
Repeated checks, critical user journeys, and predictable business rules are often good automation candidates.
However, automation requires maintenance. When an application's interface or requirements change, test scripts may need updating.
Human testing remains valuable for exploratory investigations, subjective usability judgments, and situations where the expected behavior is not fully defined.
11. How to Choose the Right Testing Coverage
Not every application needs the same testing strategy. A simple informational website has different risks from a financial platform or a large online marketplace.
The best approach depends on the application's purpose, complexity, audience, data sensitivity, and business requirements.
Identify the Application's Main Risks
Start by identifying the features that would cause the greatest harm if they failed.
For an online store, these may include checkout, payment processing, inventory, and customer accounts. For a healthcare booking platform, appointment accuracy, privacy, and access permissions may be especially important.
Testing effort should reflect the potential impact of each failure.
Define Clear Acceptance Criteria
Each feature should have clear conditions that determine whether it works correctly.
For example, a login feature might require valid users to sign in successfully, invalid credentials to be rejected, and repeated failed attempts to be handled according to the application's security policy.
Clear acceptance criteria make test results easier to evaluate and reduce disagreements between developers, testers, and stakeholders.
Combine Different Testing Methods
A comprehensive testing strategy uses several methods rather than relying on a single tool or test category.
Functional checks confirm expected behavior. Security testing identifies vulnerabilities. Performance tests measure responsiveness under load. Compatibility and accessibility testing help ensure that different users can access the application.
Regression testing then helps preserve quality as the application evolves.
Review Results and Retest Fixes
Finding a defect is only part of the process. Teams must also assess its severity, determine its cause, implement a fix, and verify the result.
After a correction, testers should repeat the failed test and consider related checks that might be affected by the change.
Tracking defects, test coverage, failure rates, and recurring issues can help teams identify areas that need additional attention.
Conclusion
Web applications must do much more than display information on a screen. They need to process data accurately, protect user accounts, respond quickly, support different devices, and remain reliable when problems occur. Testing helps development teams evaluate these responsibilities before defects create serious consequences for users or businesses.
The main areas examined by web application testing solutions include functional behavior, security, performance, compatibility, usability, accessibility, database integrity, API integrations, regression risks, and recovery capabilities. Each area reveals a different type of potential problem, making a balanced testing strategy essential.
Businesses should begin by identifying their most important features and highest risks. They can then define clear testing requirements, combine manual and automated techniques, and establish repeatable checks throughout development. Critical workflows should receive particular attention because failures in areas such as authentication, payments, or data management can have significant consequences.
It is equally important to treat testing as an ongoing activity rather than a single task completed before launch. Applications change as developers introduce features, update dependencies, and respond to new security threats. Regular testing helps ensure that these changes do not undermine existing functionality or reliability.
Ultimately, effective web application testing solutions help organizations build applications that users can trust. By detecting defects early, validating essential features, and continuously reviewing software quality, teams can reduce risks, improve usability, and support long-term business success.